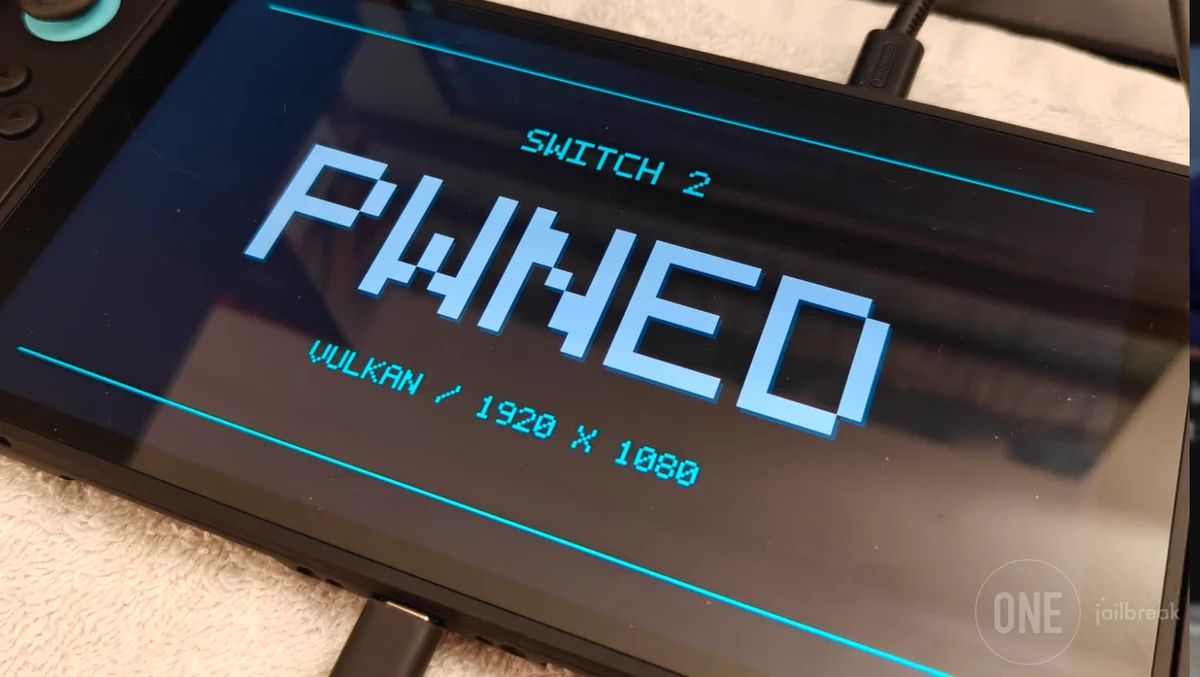
Switch 2 gets a software-only userland jailbreak through SmileBasic 4
A researcher's tethered exploit on Switch 2 firmware 23.0.1 gives userland access, enough for homebrew and mods but not kernel control.
A security researcher has a software-only partial jailbreak for the Nintendo Switch 2 on firmware 23.0.1. It gives “userland” access, which he says lets people run homebrew, reverse engineer and mod games, back up save files, and reach most of the console’s peripherals through MMIO.
The entry point is the original Switch version of SmileBasic 4, a programming environment and interpreter for Nintendo hardware. Sammy Hajhamid, who goes by Pepsipu, used OpenAI’s Codex to poke at SmileBasic’s interpreter with a custom harness. The harness sent USB commands and read the results over HDMI. After “substantial effort for ~2 weeks,” it found a 32-bit integer overflow when removing items from an array. That gave read and write access to parts of system memory.
From there he went after the sysmodules. He found a buffer overflow in the FileSystem services module that exposed a cached data pointer. That let him run “privileged filesystem actions” and eventually native code, through a faked filesystem process. The hack is at ns2jb.
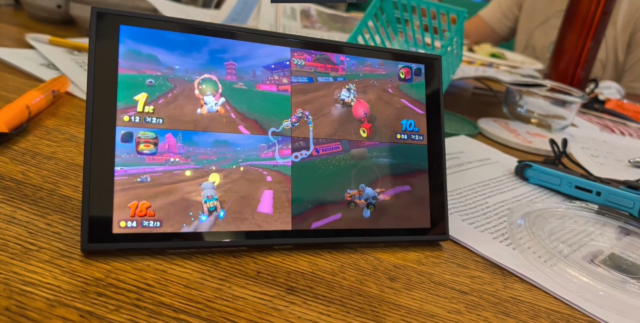
The hack is tethered. It needs a macOS or Linux PC on the same network to run a node.js package. Pepsipu showed several new modded characters in Mario Kart World as a proof of concept. Others are posting simple demos and developer tools running on exploited hardware. The access stops at userland, though, so homebrew developers stay in a small sandbox with no kernel-level control.
Nintendo pulled SmileBasic 4 from the Switch eShop worldwide. A Japanese demo that may work the same way is still up. Ars Technica thinks the bug will likely be patched in imminent firmware, which many Nintendo services and future games will require. The 2018 original Switch exploit was unpatchable and needed new hardware. This one is the softer case.
The timeline matters here: just over a year after launch, someone reached native code on the Switch 2, and the first pass through the interpreter was done with OpenAI’s Codex. After that, the usual cycle should follow, with firmware updates closing holes while people already tease exploits that use other games.