Byepervisor Reborn exploit opens PS5 hypervisor on firmware 13.60
Byepervisor Reborn, a PS5 hypervisor exploit for firmware 13.60, is out. Developers call it a base for devs. It is not a finished jailbreak.
A hypervisor exploit for PS5 firmware 13.60 is out. It’s called Byepervisor Reborn, and it works on consoles that haven’t updated to 14.00 or higher. The developers call it a base for other work, and a finished jailbreak is still missing.
The hypervisor is the layer that sits under the PS5’s system software. The exploit targets a weak spot in how the console recovers from Rest Mode. That gives read and write access to the hypervisor’s address space and turns off execute-only memory protections, so the kernel can be dumped and patched. The project’s GitHub documentation describes this.
The initial build lists support for 13.60 and 13.20, plus an untested 13.00 configuration. The underlying bug may reach back to firmware 6.xx, but the current release doesn’t cover that. Sonic-Iso first documented the bug and said it was already patched in 14.10. The developers think a modified version could work on 14.00, but none is provided, and that firmware has no public kernel exploit.
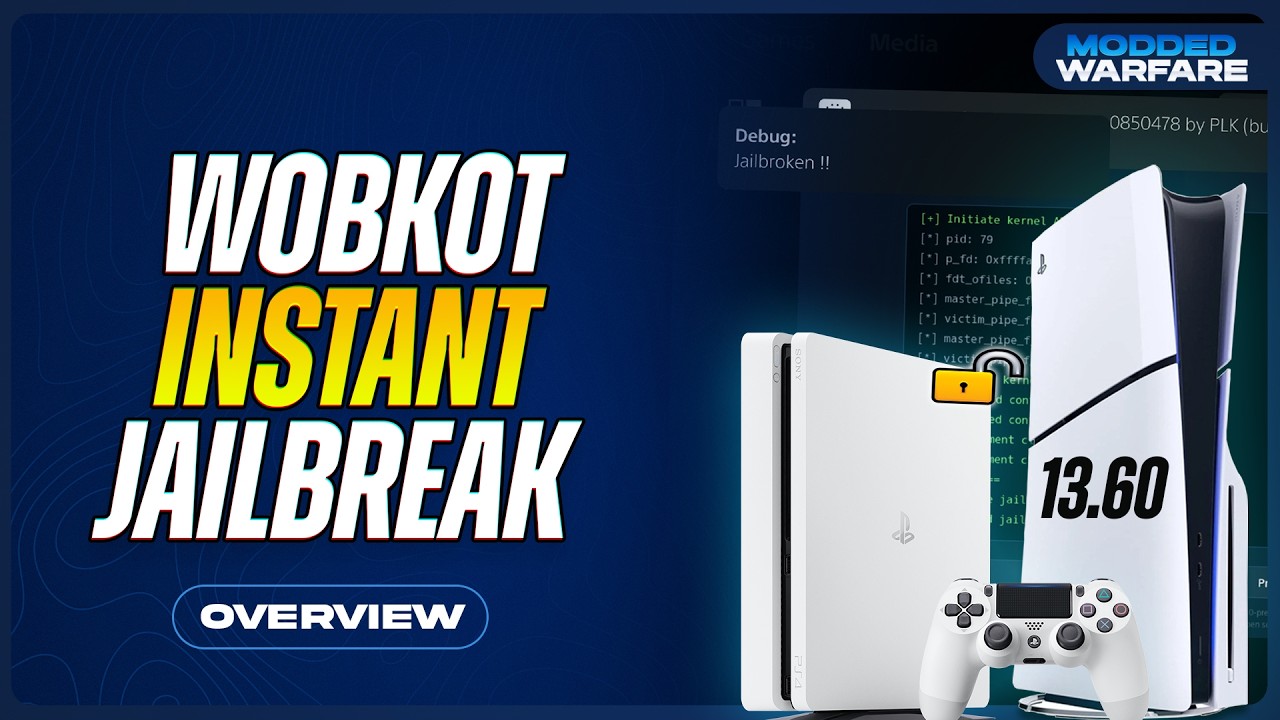
The missing piece matters most for regular users. The release ships without the homebrew-enabling patches and other parts needed for a complete jailbreak. Modding creator MODDED WARFARE covered the release on YouTube and said it removes several limits that hit jailbroken consoles. The developers put it more bluntly: the repo is not useful to regular users in its current state and is intended for developers.
The expected gains are Linux on PS5 up to firmware 13.60, where the current ceiling is 7.61, and better fake package support. The fake package part depends on code that hasn’t been released. Wccftech, a gaming news site, also says updated payloads, patches and firmware-specific testing still have to happen.
The release lands in a busy stretch for PS5 hacking. In September, the Relapse exploit, a chain of a browser bug, kernel access and an ELF loader, brought publicly accessible exploitation to 13.60. Wccftech suggests AI tools are likely fueling the pace.
The release is a new foothold for developers. It is not a finished jailbreak yet. Watch for the first payload built on top of it for 13.60, and for anyone who ports the approach to 14.00. The sources don’t list install steps, so the GitHub docs are the place to start.